Serverless & AI in brief: week 43/2026
Serverless & AI in brief is my new weekly review: every Monday I sort through the previous week’s news from AWS, serverless, AI tools and TypeScript/Node.js and explain what it means for you as
Security updates that cannot wait
</h2> <p>Three of the seven items are about security. That is no coincidence, because they are connected: the certificate incident triggered updates in browsers, runtimes and at AWS.</p> <h3>eMudhra certificates: AWS sets deadlines from October 28
</h3> <p>On October 17, Mozilla received a report that the private keys of eight intermediate certificates from the certificate authority eMudhra had been compromised. An intermediate CA issues website certificates on behalf of a root CA. With those keys, someone could create valid-looking certificates for other people’s domains. Firefox blocked the certificates the same evening, and Mozilla also removed the issuing root from its NSS certificate store. AWS followed on October 24 with Security Bulletin 2026-150-AWS: three roots are being removed from the AWS trust stores. CloudFront is scheduled to stop trusting them for origin connections from October 28, and Application Load Balancers with OIDC or JWT authentication follow from October 29 to 31. Updates are already available for Amazon Corretto, the <code>ca-certificates</code> package in Amazon Linux and botocore (version 1.43.117 and later).</p> <p>What this means for you: if a CloudFront distribution sits in front of an origin with its own certificate that was not issued through ACM, check the certificate chain before Wednesday. The same applies to identity providers behind an ALB. My article <a href="https://sascha-ms.de/en/emudhra-certificates-check-java-node-python-go?utm_source=devto&utm_medium=crosspost" rel="noopener noreferrer">eMudhra certificates: check Java, Node, Python and Go</a> shows how to check the chain in each language.</p> <h3>Node.js 26.12.1, 24.22.1 and 22.23.4 close an RCE flaw
</h3> <p>On October 21, the Node.js project released security updates for all three supported release lines. They fix ten CVEs, four of them rated “High”. The most serious is CVE-2026-111497: with manipulated input, the bundled Brotli decoder writes past the end of an internal buffer. If you decompress Brotli data from untrusted sources with <code>node:zlib</code>, the worst case is remote code execution. Security researchers have since demonstrated an exploit called “Node2Shell”. The releases also ship updated CA certificates because of the eMudhra incident.</p> <p>I would prioritize this update because it solves two problems at once. AWS updates the managed Lambda runtimes itself, but container images, CI runners, pinned runtime versions and local environments are your job. In <a href="https://sascha-ms.de/en/node2shell-cve-2026-111497-nodejs?utm_source=devto&utm_medium=crosspost" rel="noopener noreferrer">Node2Shell: close CVE-2026-111497 now</a> I describe the attack paths and how to check your Lambda functions.</p> <h3>GitHub Package Firewall checks npm packages before install
</h3> <p>Since October 20, GitHub Enterprise Cloud customers can try the new Package Firewall as a public preview. The firewall stands between your machines, CI runners or coding agents and the package registry and checks every download against rules. These include a configurable waiting period for new versions (cooldown), a lookup in the GitHub Advisory Database to see whether malware has been reported for a package, and detection of downgraded attestations. For now only npm is supported. The preview is free; later, billing will be usage-based.</p> <p>In my view, the cooldown is the biggest lever. Many supply chain attacks in recent months relied on a compromised version landing on thousands of machines within a few hours. If you let new versions sit for a few days, you simply miss most of these waves. You can adopt the principle without an Enterprise license too, for example with Dependabot’s <code>cooldown</code> option.</p> <h2>News on the Claude API and Agent Skills
</h2> <h3>Claude API 2026-10-21 rejects temperature and top_p
</h3> <p>Anthropic released API version <code>2026-10-21</code> on October 21. With it, requests containing <code>temperature</code>, <code>top_p</code> or <code>top_k</code> fail with an HTTP 400 error, even if the values match the defaults. At the same time, new major SDK versions came out that send the new version automatically, including TypeScript SDK 1.0.0, Python SDK 2.0.0 and Java SDK 3.0.0. They bring breaking changes of their own: the API key is now sent as <code>Authorization: Bearer</code> instead of <code>X-Api-Key</code>, and the license switches from MIT to Apache 2.0. On Amazon Bedrock, the new version only works with Claude 4.7 and newer.</p> <p>My advice: do not let Dependabot auto-merge PRs for <code>@anthropic-ai/sdk</code> this time. First search your code for sampling parameters and check whether a gateway, proxy or log filter depends on the old header. You will find the individual steps with code examples in <a href="https://sascha-ms.de/en/claude-api-2026-10-21-migration-new-sdk?utm_source=devto&utm_medium=crosspost" rel="noopener noreferrer">Claude API 2026-10-21: migrating to the new SDK</a>.</p> <h3>Agent Skills move to the Agentic AI Foundation
</h3> <p>On October 22, Anthropic handed Agent Skills over to the Agentic AI Foundation, a foundation within the Linux Foundation. Behind the term is a simple format: a <code>SKILL.md</code> in a folder, optionally with scripts, that gives an AI agent domain knowledge and workflows. Besides the specification, the name and logo, the project’s GitHub account and agentskills.io change hands as well. According to Anthropic, more than 70 agent platforms have adopted the standard since December 2025, including ChatGPT, Cursor, GitHub Copilot and VS Code. Going forward, people from several companies will maintain it, among them Anthropic, Google and OpenAI. Versioned releases, a formal process for change proposals and security guidelines are planned.</p> <p>MCP took the same path before, and I think it is the right one. A standard that no single vendor owns makes it easier to invest time in good skills. I show how to write a <code>SKILL.md</code> that works across several agents in <a href="https://sascha-ms.de/en/write-agent-skills?utm_source=devto&utm_medium=crosspost" rel="noopener noreferrer">Writing Agent Skills</a>.</p> <h2>Serverless, AWS and TypeScript
</h2> <h3>CloudFormation Force Rollback rescues stuck stacks
</h3> <p>Since October 22, CloudFormation offers a force rollback option when you continue an update rollback. Until now, for a stack in the <code>UPDATE_ROLLBACK_FAILED</code> state you had to name and skip every stuck resource individually. Now CloudFormation does this in one step and returns the stack to a state you can deploy from again. Resources that still need attention are recorded. The feature is available in all Regions at no extra cost and also works with the AWS CDK, the CLI and the SDKs.</p> <p>Anyone who has spent a night in front of a stuck stack will appreciate this. Still, force rollback is the emergency exit, not the normal case. Afterwards the stack no longer matches the template exactly, so before your next deploy a drift-aware change set that shows you the differences is worth it. The commands are in <a href="https://sascha-ms.de/en/cloudformation-update-rollback-failed-force-rollback?utm_source=devto&utm_medium=crosspost" rel="noopener noreferrer">UPDATE_ROLLBACK_FAILED: rescue a stack with force rollback</a>.</p> <h3>TypeScript 7.1 Beta type-checks up to 47 percent faster
</h3> <p>Microsoft released the beta of TypeScript 7.1 on October 20, the first feature release since the switch to the native compiler in 7.0. In the TypeScript team’s benchmarks, type-checking time drops by 13 to 47 percent compared to 7.0, depending on the project, and memory usage by 16 to 50 percent. In addition, <code>es2026</code> is now a stable value for <code>--target</code> and <code>--lib</code>, and the compiler API is split into several entry points such as <code>typescript/sync</code> and <code>typescript/ast</code>. The release candidate is expected about a month after the beta.</p> <p>Trying it out costs you little: run <code>npm install -D typescript@beta</code> on a separate branch and let your CI run. Keep an eye on tools built on the compiler API, such as linter plugins or framework checkers. The most important changes and a test guide are in <a href="https://sascha-ms.de/en/typescript-7-1-beta?utm_source=devto&utm_medium=crosspost" rel="noopener noreferrer">Testing TypeScript 7.1 Beta</a>.</p> <h2>My takeaways from Serverless & AI in brief, week 43
</h2> <p>This week shows nicely how closely the topics are intertwined by now. A problem at a certificate authority reaches browsers, Node.js, Java and AWS within a few days. Meanwhile, tools for AI agents are growing up: open standards, versioned APIs and real breaking changes come with the same duties we know from every other dependency.</p> <p>If you only have half an hour, I would go in this order:</p> <ol> <li>Before October 28, check the certificate chains of CloudFront origins and of identity providers behind ALBs.</li> <li>Upgrade Node.js to 26.12.1, 24.22.1 or 22.23.4 everywhere, including containers and CI.</li> <li>Plan Claude SDK upgrades deliberately instead of merging them automatically.</li> <li>Introduce a waiting period for new npm versions, with the Package Firewall or with Dependabot.</li> </ol> <h2>What comes next in Serverless & AI in brief
</h2> <p>The next review will appear on Monday, November 2, and covers week 44. I collect all issues on the page <a href="https://sascha-ms.de/en/series/serverless-ai-in-brief?utm_source=devto&utm_medium=crosspost" rel="noopener noreferrer">Series: Serverless & AI in brief</a>. I would rather include four good items than seven thin ones. If you think an important piece of news is missing, feel free to add it in the comments.</p> <p>Now over to you: which of these seven items actually created work for your team this week?</p> <h2>Sources
</h2> <ul> <li><a href="https://blog.mozilla.org/security/2026/10/20/protecting-firefox-users-following-the-compromise-of-emudhra-intermediate-certificates/" rel="noopener noreferrer">Mozilla Security Blog: Protecting Firefox users following the compromise of eMudhra intermediate certificates</a></li> <li><a href="https://aws.amazon.com/security/security-bulletins/rss/2026-150-aws/" rel="noopener noreferrer">AWS Security Bulletin 2026-150-AWS</a></li> <li><a href="https://nodejs.org/en/blog/vulnerability/october-2026-security-releases" rel="noopener noreferrer">Node.js: October 2026 Security Releases</a></li> <li><a href="https://www.imperva.com/blog/node2shell-from-brotli-data-to-remote-code-execution/" rel="noopener noreferrer">Imperva: Node2Shell – From Brotli Data to Remote Code Execution</a></li> <li><a href="https://github.blog/changelog/2026-10-20-github-package-firewall-in-public-preview" rel="noopener noreferrer">GitHub Changelog: GitHub Package Firewall in public preview</a></li> <li><a href="https://platform.claude.com/docs/en/release-notes/overview" rel="noopener noreferrer">Claude Platform: Release Notes</a></li> <li><a href="https://platform.claude.com/docs/en/api/migration-2026-10-21" rel="noopener noreferrer">Claude Platform: Migrating to API version 2026-10-21</a></li> <li><a href="https://www.anthropic.com/news/donating-agent-skills-to-the-agentic-ai-foundation" rel="noopener noreferrer">Anthropic: Donating Agent Skills to the Agentic AI Foundation</a></li> <li><a href="https://aws.amazon.com/about-aws/whats-new/2026/10/aws-cloudformation-cdk/" rel="noopener noreferrer">AWS What’s New: CloudFormation force rollback</a></li> <li><a href="https://devblogs.microsoft.com/typescript/announcing-typescript-7-1-beta/" rel="noopener noreferrer">TypeScript Blog: Announcing TypeScript 7.1 Beta</a></li> </ul> <p><em>This post was created with AI assistance.</em></p> <p>👉 <strong>Next step:</strong> Working with AWS CDK? Grab my printable <a href="https://sascha-ms.de/en/cheat-sheets/aws-cdk/?utm_source=devto&utm_medium=crosspost" rel="noopener noreferrer">AWS CDK cheat sheet</a> with commands, concepts and a stack skeleton.</p> <p><em>Originally published on <a href="https://sascha-ms.de/en/serverless-ai-in-brief-week-43-2026?utm_source=devto&utm_medium=crosspost" rel="noopener noreferrer">sascha-ms.de</a>.</em> More articles on serverless, AI in everyday development and leading tech teams: <a href="https://sascha-ms.de/en/?utm_source=devto&utm_medium=crosspost" rel="noopener noreferrer">sascha-ms.de/en</a></p>Original source
Tags
Related Articles
Continue reading with these similar posts

Sources: Missouri RB Hardy, shot in offseason, to return vs. Arkansas
Missouri All-America tailback Ahmad Hardy is set to make his season debut for the Tigers this weekend at Arkansas, sources told ESPN.

Red Wings suspend Larkin as team explores trade options; players keen to move on
The Red Wings announced Thursday that star forward Dylan Larkin has been suspended without pay after informing the team he no longer wanted to play for Detroit.

Packers' Jacobs says TD celebration was ode to gospel song, not mocking arrest
The Packers' Josh Jacobs said he was surprised his first-half TD celebration was perceived by some as mocking his May arrest, saying it was an ode to a gospel song.

Israel faces weeks of coalition haggling as Netanyahu’s party claims election 'stolen'
Israel's election leaves the country facing weeks of coalition bargaining and an uphill battle for the opposition party to form a majority government.
Herdr has released native app
Comments
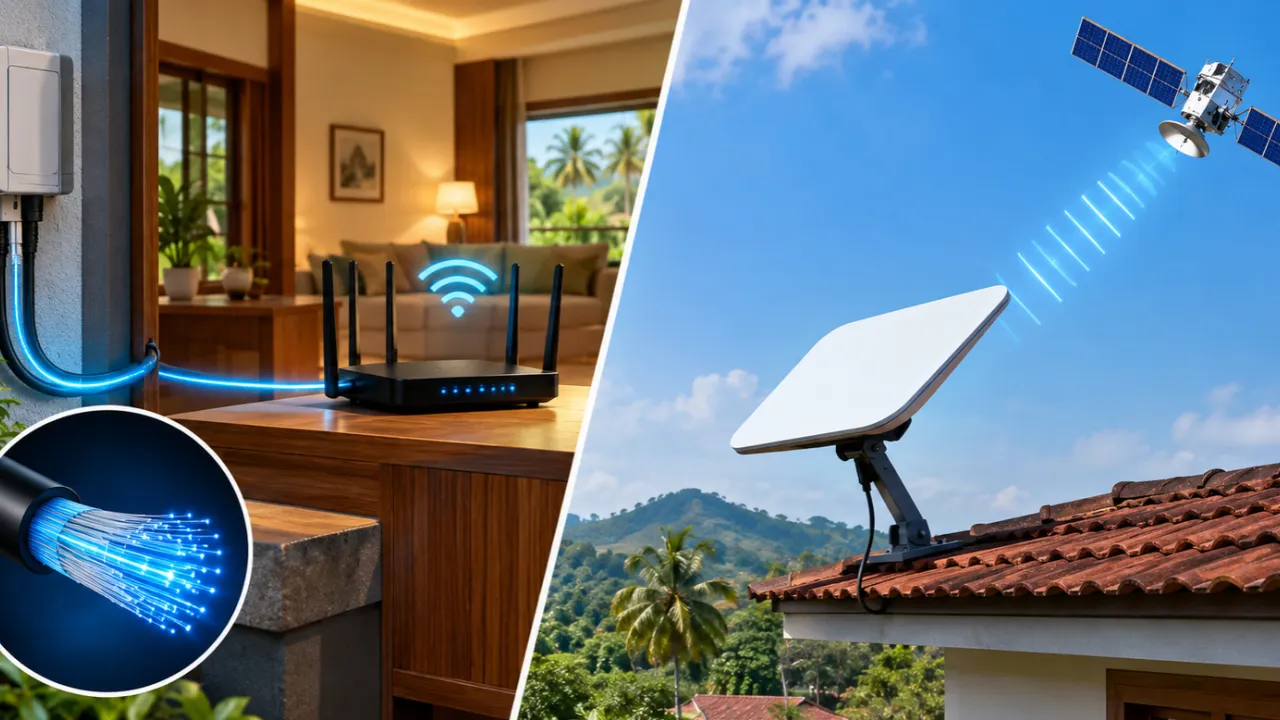
Satellite vs Fiber Internet: ഇന്ത്യയുടെ ഇന്റർനെറ്റ് വിപ്ലവത്തിന് ആര് മികച്ചത്?
ഇന്ന് ഇന്റർനെറ്റ് ഒഴിച്ചുകൂടാനാവാത്ത ഭാഗമായി മാറിക്കഴിഞ്ഞു. ഇപ്പോൾ ഇന്ത്യയിൽ നിലവിൽ ഏറ്റവും ജനപ്രിയമായ ഇന്റർനെറ്റ് മാധ്യമം ഒപ്റ്റിക്കൽ ഫൈബർ (Fiber Internet) ആണ്. എന്നാൽ രാജ്യത്ത് സജീവ ചർച്ചയായി മാറിക്